Federal Cybersecurity Mandates 2026: Small Business Guide
Anúncios
New federal cybersecurity mandates for small businesses in 2026 necessitate immediate action to understand compliance requirements and implement necessary protective measures within the next three months.
The digital landscape is constantly evolving, and with it, the threats posed by cybercriminals. For small businesses, staying ahead of these threats isn’t just good practice; it’s becoming a legal imperative. The upcoming federal cybersecurity mandates impacting small businesses in 2026 are set to redefine how companies approach their digital defenses, and understanding these changes in the next three months is absolutely critical.
Understanding the New Regulatory Landscape
The federal government is intensifying its focus on cybersecurity across all sectors, recognizing that small businesses, while often overlooked, represent a significant and vulnerable link in the nation’s digital infrastructure. These new mandates are designed to create a more resilient and secure national economy by standardizing baseline cybersecurity practices.
Historically, many small businesses operated with minimal or ad-hoc cybersecurity measures, often due to perceived cost or complexity. However, the escalating frequency and sophistication of cyberattacks have prompted a fundamental shift in regulatory thinking. The goal is to move beyond voluntary guidelines to enforceable standards, ensuring a foundational level of protection for sensitive data and critical operations.
Why Small Businesses Are a Target
Cybercriminals often view small businesses as easier targets than larger corporations, which typically have more robust security budgets and dedicated IT teams. This makes small businesses attractive entry points for broader supply chain attacks or for harvesting valuable data with less resistance.
- Limited Resources: Smaller budgets and fewer IT staff often mean less sophisticated security tools and practices.
- Valuable Data: Small businesses still handle sensitive customer data, financial information, and intellectual property.
- Supply Chain Weakness: Attacking a small vendor can provide access to a larger, more secure client.
These new mandates aim to close these gaps, compelling small businesses to elevate their security posture. Ignoring these upcoming requirements is not an option, as non-compliance could lead to severe penalties, reputational damage, and operational disruptions.
In essence, the new regulatory landscape reflects a national security imperative. By ensuring that even the smallest entities adhere to basic cybersecurity protocols, the government seeks to bolster the collective defense against cyber threats, protecting both individual businesses and the broader economic ecosystem.
Key Components of the 2026 Mandates
The upcoming federal cybersecurity mandates for 2026 are comprehensive, touching upon several critical areas of digital security. While specific details are still being finalized and disseminated, the overarching themes revolve around proactive defense, incident response, and continuous improvement.
At their core, these mandates are designed to establish a consistent, minimum standard for cybersecurity hygiene. They move beyond simple recommendations, introducing enforceable requirements that small businesses must integrate into their daily operations. This shift demands a more structured and formalized approach to digital security.
Mandatory Security Controls
One of the primary components involves the implementation of specific security controls. These are not merely suggestions but will likely become non-negotiable elements of a compliant cybersecurity framework.
- Multi-Factor Authentication (MFA): Requiring more than one method to verify a user’s identity, significantly reducing unauthorized access.
- Regular Backups: Implementing robust data backup and recovery plans to mitigate the impact of data loss due to cyberattacks or system failures.
- Endpoint Protection: Ensuring all devices connected to the network (laptops, desktops, mobile devices) have adequate security software and configurations.
- Network Segmentation: Dividing network into smaller, isolated segments to limit the spread of attacks.
These controls are foundational. Their effective implementation will require not just technology, but also policy development and employee training. The mandates will likely specify standards for documenting these controls and demonstrating their ongoing effectiveness.
Incident Response and Reporting
Another crucial aspect is the emphasis on incident response. It’s no longer enough to try and prevent attacks; businesses must also be prepared to react swiftly and effectively when an incident occurs. This includes clear protocols for detection, containment, eradication, and recovery.
Furthermore, the mandates are expected to include strict reporting requirements. Small businesses will likely be obligated to report cybersecurity incidents to relevant federal agencies within a specified timeframe. This ensures that federal authorities can monitor the threat landscape and provide assistance where necessary, but also places a significant burden on businesses to have mature incident detection capabilities.
Understanding these key components now allows businesses to begin auditing their current systems and identifying areas that require immediate attention to meet the 2026 compliance deadline.
Assessing Your Current Cybersecurity Posture
Before any significant changes can be made, small businesses must conduct a thorough assessment of their existing cybersecurity posture. This involves understanding what assets need protection, what vulnerabilities currently exist, and what processes are already in place.
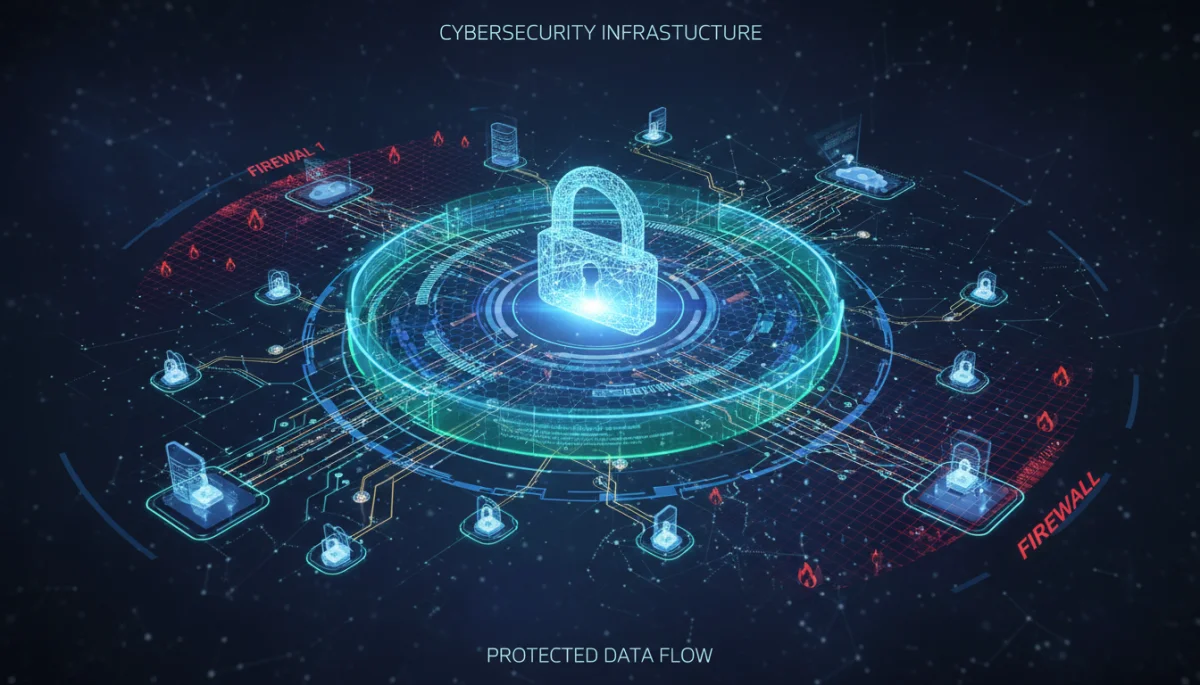
Think of this assessment as a digital health check-up. Just as you wouldn’t start a major renovation without knowing the current state of your building, you shouldn’t attempt to comply with new mandates without a clear picture of your current cybersecurity strengths and weaknesses.
Conducting a Risk Assessment
A comprehensive risk assessment is the cornerstone of effective cybersecurity planning. This involves identifying potential threats, evaluating their likelihood and impact, and prioritizing which risks to address first.
- Identify Critical Assets: What data, systems, and processes are essential to your business operations?
- Evaluate Existing Controls: What security measures are currently in place to protect these assets?
- Identify Vulnerabilities: Are there any weaknesses in your systems, software, or human processes that could be exploited?
- Assess Threat Landscape: What specific cyber threats are most relevant to your industry and business size?
Tools and frameworks like the NIST Cybersecurity Framework can provide a structured approach to this assessment, helping businesses systematically evaluate their current state against recognized best practices. This step is not just about compliance, but about genuinely improving your resilience.
Gap Analysis and Remediation Planning
Once the risk assessment is complete, the next step is to perform a gap analysis. This involves comparing your current cybersecurity posture against the anticipated 2026 federal mandates. Where are the discrepancies? What needs to be improved or implemented?
Following the gap analysis, a detailed remediation plan must be developed. This plan should outline specific actions, responsible parties, timelines, and required resources for addressing each identified gap. Prioritize actions based on the severity of the risk and the urgency of the mandate. This proactive planning in the next three months will be instrumental in ensuring a smooth transition to compliance.
By systematically assessing risks and planning for remediation, small businesses can approach the new mandates with a clear strategy, rather than reacting haphazardly as the deadline approaches.
The Role of Technology and Tools
Meeting the new federal cybersecurity mandates will undoubtedly require leveraging appropriate technology and tools. While policies and training are crucial, the right technological infrastructure forms the backbone of a strong defense. Small businesses need to be strategic in their investments, focusing on solutions that offer both efficacy and ease of management.
The market is flooded with cybersecurity products, making it challenging for small businesses to choose wisely. The key is to select tools that align with the specific requirements of the mandates and are scalable to the business’s needs, without overcomplicating operations or exceeding budget constraints.
Essential Cybersecurity Solutions
Certain types of technology will become indispensable for compliance. These aren’t luxury items but fundamental defenses against modern cyber threats.
- Firewalls and Intrusion Detection Systems (IDS): To monitor and control network traffic, blocking unauthorized access attempts.
- Antivirus and Anti-Malware Software: Continuously protecting endpoints from malicious software.
- Secure Email Gateways: Filtering out phishing attempts, spam, and malicious attachments before they reach inboxes.
- Data Encryption: Protecting sensitive data both in transit and at rest, rendering it unreadable to unauthorized parties.
- Security Information and Event Management (SIEM): While often complex, simpler versions can help aggregate and analyze security logs for early threat detection.
Investing in these solutions is not just about ticking boxes for compliance; it’s about building a robust, multi-layered defense. The mandates will likely require demonstrable proof that these technologies are not only implemented but also actively managed and updated.
Cloud Security and Vendor Management
Many small businesses rely heavily on cloud services for data storage, applications, and infrastructure. The mandates will extend to how these cloud environments are secured and how third-party vendors are managed. Businesses must ensure that their cloud providers meet federal security standards and that contracts include appropriate cybersecurity clauses.
Vendor risk management will become a critical task. Small businesses will need to assess the cybersecurity posture of all their third-party service providers, as a vulnerability in a vendor’s system can directly impact their own compliance and security. This means reviewing service level agreements (SLAs) and conducting due diligence on vendor security practices.
The right technology, coupled with careful vendor management, will empower small businesses to meet the technical demands of the 2026 federal cybersecurity mandates efficiently and effectively.
Training and Awareness: Your Human Firewall
Even the most sophisticated cybersecurity technology can be rendered ineffective if employees are not adequately trained and aware of best practices. The human element remains the weakest link in many security chains, and the new federal mandates are expected to place significant emphasis on human-centric security measures.
Think of your employees as your first line of defense. They are the ones interacting with emails, clicking links, and handling sensitive data daily. Equipping them with the knowledge and skills to identify and respond to threats is just as important as deploying firewalls or encryption.
Mandatory Employee Cybersecurity Training
The 2026 mandates will likely require regular, mandatory cybersecurity training for all employees, regardless of their role. This training should not be a one-time event but an ongoing process that adapts to evolving threats and technologies.
- Phishing Awareness: Teaching employees how to recognize and report phishing emails and other social engineering tactics.
- Password Hygiene: Emphasizing the importance of strong, unique passwords and the use of password managers.
- Data Handling Protocols: Educating staff on how to properly handle, store, and transmit sensitive company and customer data.
- Incident Reporting: Ensuring employees know the correct procedures for reporting suspicious activities or potential security breaches.
Effective training goes beyond simply presenting information; it involves interactive sessions, realistic simulations, and clear communication. The goal is to foster a culture of security awareness where every employee understands their role in protecting the business.
Developing a Culture of Security
Beyond formal training, creating a strong security culture is paramount. This involves integrating security considerations into daily operations and decision-making processes. It means that cybersecurity is not just an IT department’s responsibility, but a shared commitment across the entire organization.
Leadership plays a crucial role in championing this culture by demonstrating their commitment to security and providing the necessary resources. Regular communication about new threats, security updates, and policy changes helps keep cybersecurity top of mind for everyone. This proactive approach to human factors will be a distinguishing feature of businesses that successfully comply with the upcoming mandates.
By investing in comprehensive training and fostering a robust security culture, small businesses can build a powerful ‘human firewall’ that significantly enhances their overall cybersecurity posture and meets the federal requirements.
Timeline and Next Steps for Small Businesses
The clock is ticking, and with the 2026 federal cybersecurity mandates on the horizon, small businesses have a critical window of opportunity to prepare. The next three months are crucial for laying the groundwork for compliance, ensuring that your business is not caught off guard.
Procrastination can be costly. Starting early allows for thorough planning, budgeting, and implementation, minimizing disruption to operations and avoiding last-minute panic. A phased approach will be more effective than attempting to overhaul everything at once.
Immediate Actions (Next 3 Months)
Focusing on these immediate steps will set your business on the right path towards compliance and enhanced security.
- Assign a Cybersecurity Lead: Designate a person or team responsible for overseeing compliance efforts, even if it’s an existing employee with added responsibilities.
- Conduct an Initial Assessment: Perform a high-level review of your current cybersecurity practices against known or anticipated mandate requirements.
- Budget Allocation: Begin allocating financial resources for necessary technology upgrades, training, and potential expert consultations.
- Seek Expert Guidance: Consider consulting with cybersecurity professionals who specialize in small business compliance to interpret complex regulations.
- Employee Awareness Campaign: Start informal awareness campaigns to sensitize staff to the importance of cybersecurity.
These initial steps are about gaining clarity and momentum. They are foundational to the more extensive work that will be required over the coming months and years leading up to 2026.
Long-Term Strategy (Beyond 3 Months)
While the immediate focus is on the next three months, compliance with the 2026 mandates is an ongoing journey. A long-term strategy is essential for sustained security and adherence to evolving regulations.
This includes regularly updating security policies, conducting periodic risk assessments, continuous employee training, and investing in advanced security technologies as your business grows and threats evolve. Establishing a culture of continuous improvement in cybersecurity will not only ensure compliance but also provide a competitive edge in a digital-first economy.
By taking decisive action in the next three months and committing to a long-term strategy, small businesses can transform the challenge of federal cybersecurity mandates into an opportunity for greater resilience and trust.
| Key Point | Brief Description |
|---|---|
| Regulatory Shift | Federal government is moving from voluntary guidelines to mandatory cybersecurity standards for small businesses by 2026. |
| Core Mandates | Includes mandatory security controls (MFA, backups) and strict incident response/reporting requirements. |
| Preparation Urgency | Small businesses have three crucial months to assess current posture, plan remediation, and allocate resources. |
| Human Element | Mandatory employee training and fostering a strong security culture are essential for effective compliance. |
Frequently Asked Questions About 2026 Cybersecurity Mandates
The main goals are to enhance the national cybersecurity posture by establishing baseline security standards for small businesses, reduce their vulnerability to cyberattacks, protect critical data, and ensure a more resilient digital infrastructure across the economy. These mandates aim to close existing security gaps.
Small businesses will need to implement mandatory security controls like MFA and regular backups, develop robust incident response plans, and comply with strict reporting requirements. This will necessitate investments in technology, employee training, and potentially external cybersecurity expertise to meet the new federal standards.
In the next three months, small businesses should prioritize conducting a comprehensive risk assessment, identifying a cybersecurity lead, allocating a budget for necessary upgrades, and starting initial employee cybersecurity awareness training. Seeking expert guidance can also clarify complex regulatory details.
Non-compliance could lead to significant financial penalties, legal liabilities, reputational damage, and loss of customer trust. Furthermore, a lack of adequate cybersecurity measures increases the risk of successful cyberattacks, resulting in data breaches, operational downtime, and severe business disruption.
Small businesses can leverage resources from agencies like NIST (National Institute of Standards and Technology), CISA (Cybersecurity and Infrastructure Security Agency), and the Small Business Administration (SBA). Consulting with specialized cybersecurity firms or local business development centers can also provide tailored guidance and support.
Conclusion
The impending federal cybersecurity mandates for small businesses in 2026 represent a significant shift in the regulatory landscape, underscoring the critical importance of robust digital defenses. While these new requirements may seem daunting, they offer an unparalleled opportunity for small businesses to strengthen their security posture, protect their valuable assets, and build greater trust with their customers and partners. The next three months are not merely a countdown to compliance; they are a vital period for proactive assessment, strategic planning, and foundational implementation. By embracing these changes now, small businesses can transform potential challenges into sustainable advantages, ensuring their resilience and longevity in an increasingly interconnected and threat-filled digital world.
